In today's evolving cybersecurity landscape, businesses face complex threats that require specialized expertise to manage effectively. A Virtual Chief Information Security Officer (vCISO) provides organizations with the leadership and guidance needed to navigate these challenges without the need for a full-time, in-house CISO. This is particularly important for organizations preparing for NIS2 compliance ahead of the deadlines set for the baseline measures.
What Is a Virtual CISO?
A Virtual CISO is an experienced cybersecurity professional who works remotely with businesses to develop and implement security strategies. They offer the same level of expertise as a traditional CISO but on a flexible, on-demand basis, making it a cost-effective solution for companies of all sizes. For organizations subject to NIS2, a Virtual CISO can help implement the baseline security measures required by the Italian Cybersecurity Agency (ACN).
Key Benefits of a Virtual CISO
A Virtual CISO brings several advantages to an organization, including:
- Strategic leadership to align cybersecurity with business goals.
- Comprehensive risk assessments and mitigation strategies.
- Access to cutting-edge threat intelligence and best practices.
- Cost savings compared to hiring a full-time CISO.
By leveraging a Virtual CISO, businesses can enhance their security posture while staying within budget. This is especially valuable for organizations following our detailed guide to NIS 2 compliance.
Is a Virtual CISO Right for Your Business?
A Virtual CISO is an ideal solution for businesses that:
- Operate in highly regulated industries with strict compliance requirements.
- Lack the internal resources to manage cybersecurity effectively.
- Need expert guidance to handle complex security challenges.
Whether you're a growing startup or an established enterprise, a Virtual CISO can provide the expertise needed to stay secure in a dynamic threat landscape. For organizations preparing for NIS2 compliance, a Virtual CISO can be instrumental in meeting the directive's requirements and implementing the necessary security measures.
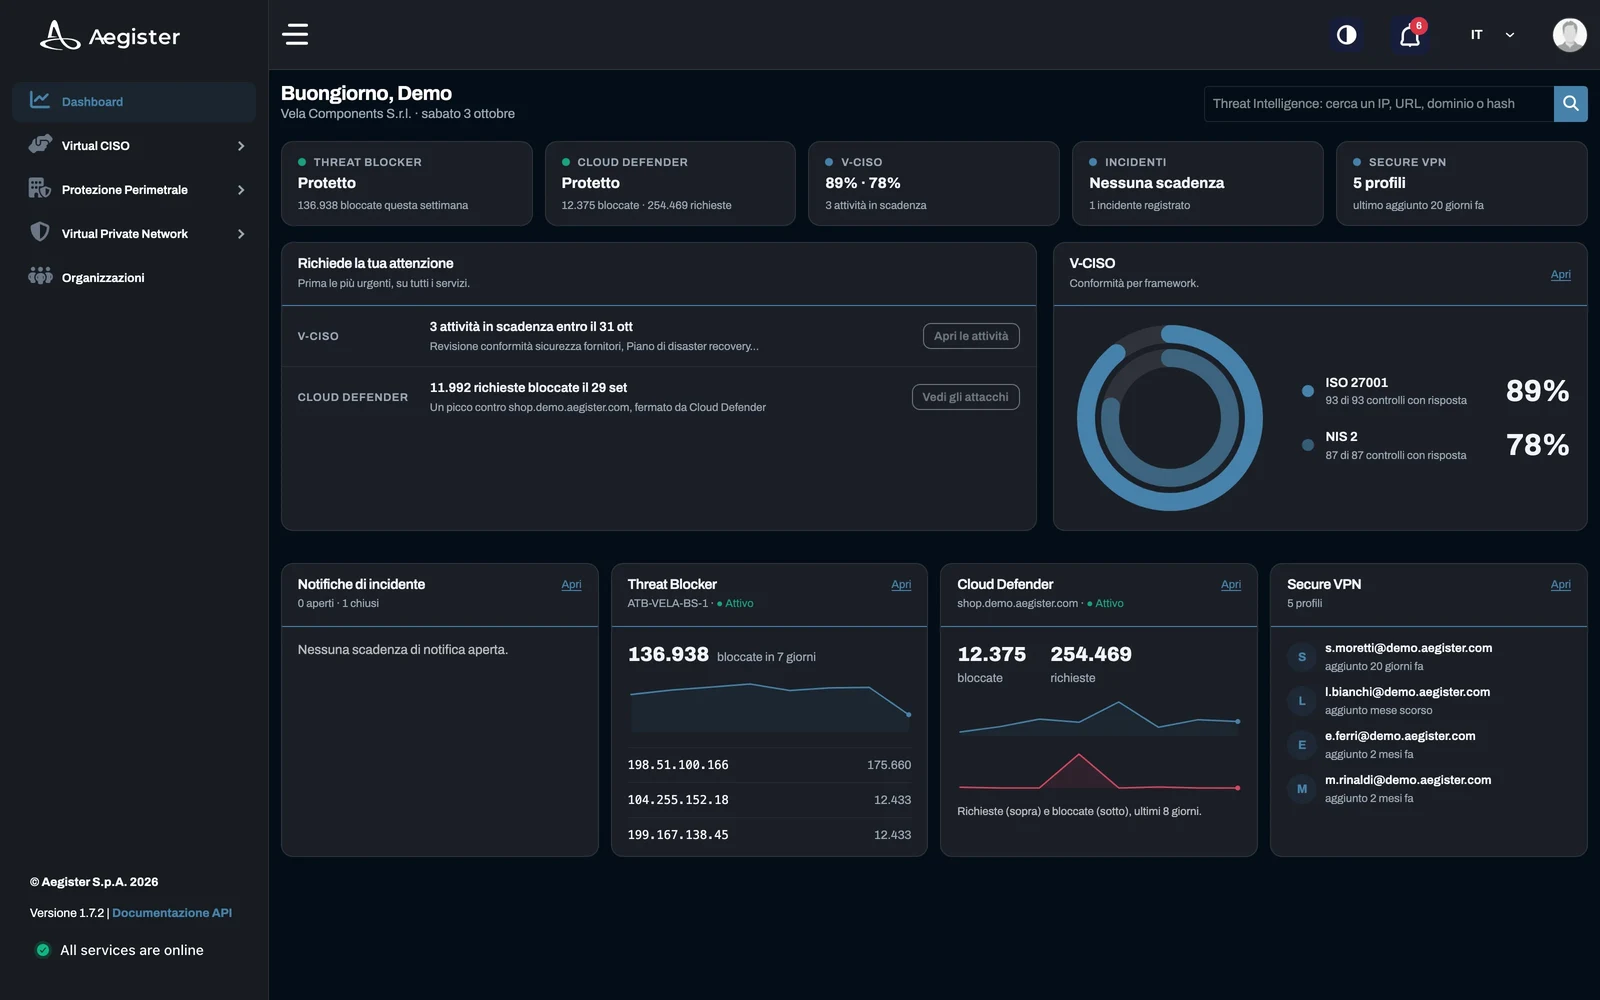
Discover the Aegister Virtual CISO service: external CISO leadership for SMEs and regulated organizations, delivered through Cyber Console with transparent reporting and flexible plans.