

NIS 2 documentation audit
A review of the documentation NIS 2 requires, with the findings and a plan to close the gaps.
Voucher MIMIT code VCCFA2600000933-D9How it works
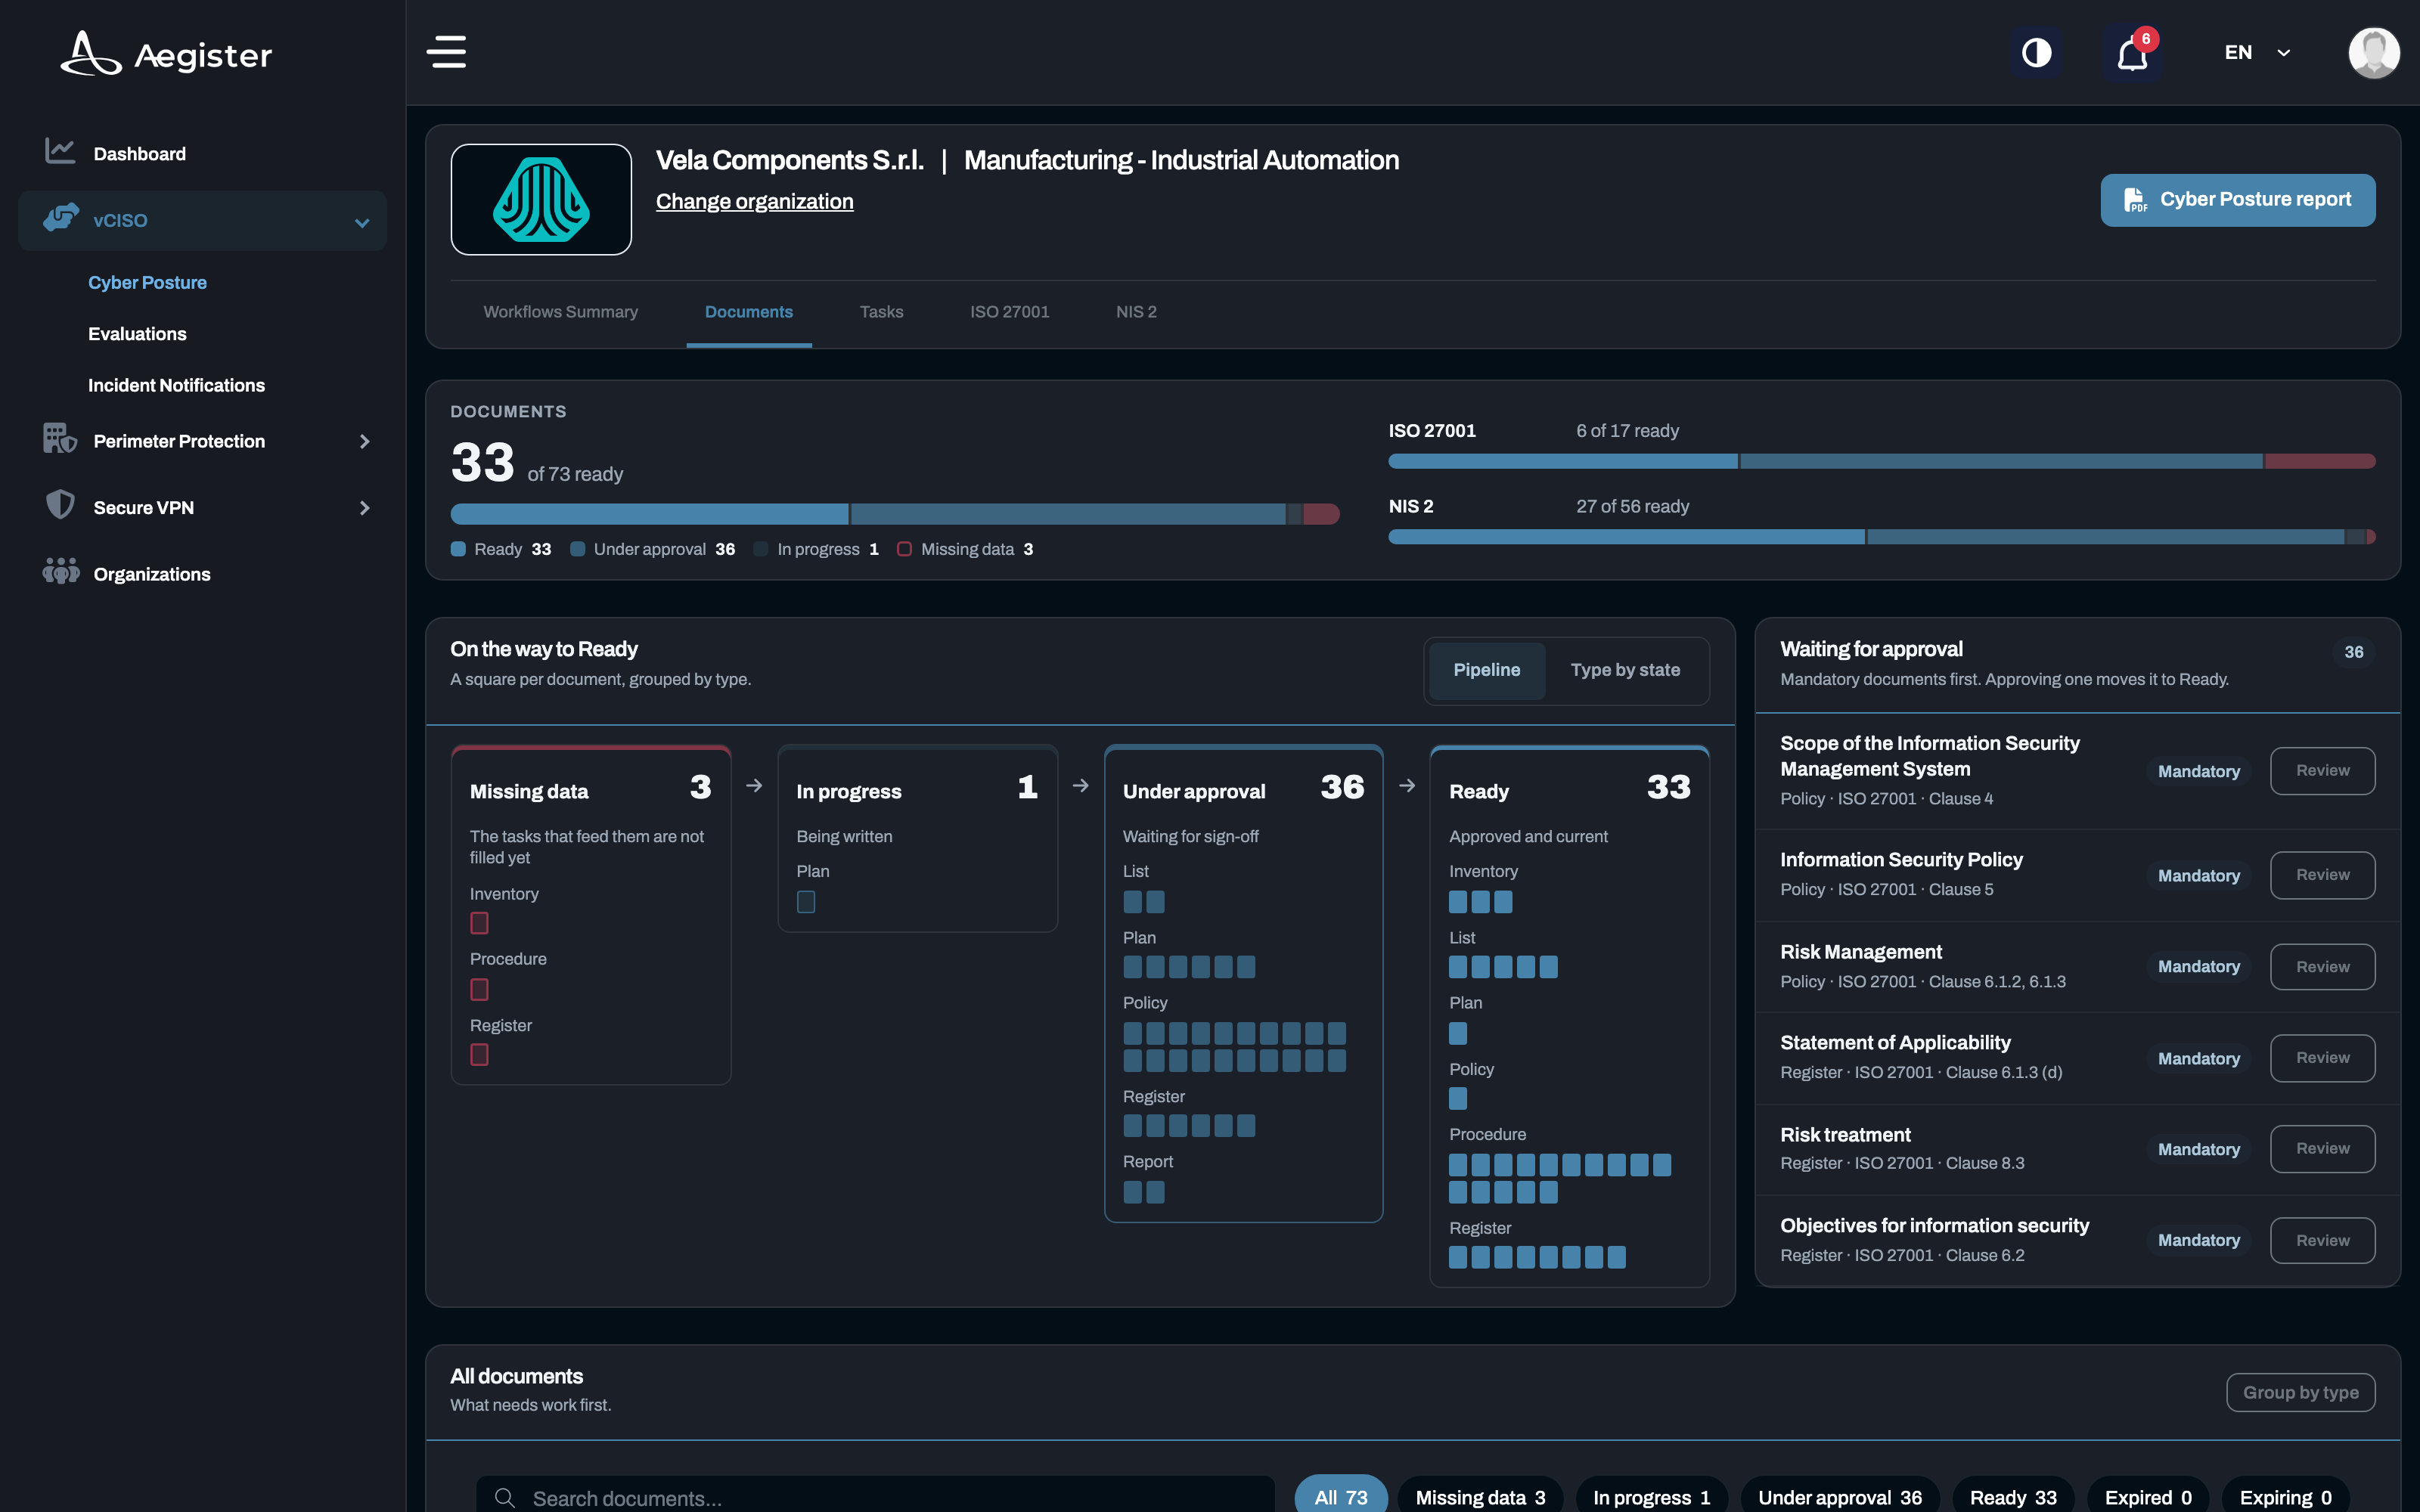
We check the documents NIS 2 requires one by one: missing or incomplete ones become findings, each with its severity, and the findings become the corrective action plan in order of priority.
-
1
Document review
We collect your existing documentation and compare it with what NIS 2 requires, category by category.
-
2
Findings
For each missing or incomplete document we record the requirement it relates to and the severity of the finding.
-
3
Corrective action plan
The findings become corrective actions in order of priority, with timing, owners and checkpoints.
6-category model
A structured framework to verify every aspect of NIS 2 documentation compliance, aligned with NIST CSF functions.
Govern
Policies, roles, responsibilities and organizational structure for information security.
Identify
Asset inventories, risk assessment and critical dependency mapping.
Protect
Technical and organizational protection measures: access controls, training, supply chain security.
Detect
Event monitoring, anomaly detection and security indicator analysis procedures.
Respond
Incident management, reporting, investigation, containment and threat eradication.
Recover
Business continuity, disaster recovery and recovery plans for organizational resilience.
Assessment methodology
A structured and repeatable approach to assess the documentation maturity of your organization.
Scoring
Each category gets a normalised score, compared against a stated conformity threshold.
Finding severity
Each finding is given a severity, and that severity sets the order of the corrective actions.
Gap analysis
Missing or incomplete documents are listed with the legal requirement each one answers to.
What you get
The documents we hand over when the check is done.
Executive summary
A summary for management with the state of conformity, the main risks and the priorities to address.
Findings in detail
For each category: the evidence collected, the documents missing and what it takes to complete them.
Corrective action plan
Corrective actions in priority order, with timings, owners and checkpoints.
Ready-to-use documentation
Policies, procedures, registers and operational plans already structured and aligned with NIS 2 requirements, generated directly from the platform.
Security policies · Remediation plan · Supplier register · Business continuity plan · Incident handling · Risk assessment · Training plan · Disaster recovery
Documentation audit insights
Guides and insights on documentation audit, baseline compliance and NIS 2 readiness.
 Made with AI
10 October 2026
ACN supervision under NIS 2: inspections, orders and fines
For entities placed on the NIS list in April 2025, ACN gives October 2026 as the deadline for the baseline measures. How ACN supervises after that: monitoring and self-assessments, ex ante inspections for essential entities and ex post for important ones, orders and formal notices, fines up to 2% of turnover. With the deadlines for each cohort, late registrations included, and a checklist for the evidence file.
 Made with AI
9 October 2026
NIS 2 assessment: a self-assessment checklist for SMEs
Your company has just found out it falls under NIS 2. A self-assessment to run before an ACN review or an external audit: confirm scope, find the measures for essential or important entities, answer a checklist by function with the evidence for each question, score the gaps and decide what to fix first.
 Made with AI
8 October 2026
NIS 2 vs ISO 27001: what certification covers and the gaps
Your company holds or plans ISO/IEC 27001 and falls under NIS 2. What the certification already covers, the obligations D.Lgs. 138/2024 adds (registration, management body accountability, notification to CSIRT Italia, the ACN baseline measures, supply chain) and a control mapping to reuse the ISMS without doing the work twice.