


NIS 2 Directive
We guide you to compliance with the NIS 2 Directive and D.Lgs. 138/2024.
Voucher MIMIT code VCCFA2600000933-D9How it works
We take you to NIS 2 compliance in three phases: we check the scope, measure the gaps against the controls and guide you as you put the measures in place, with activities, documents and evidence on Cyber Console.
-
1
NIS 2 scope check
We check whether your company is in scope of NIS 2, as an essential or important entity, from its sector and size.
-
2
Gap analysis
We assess the NIS 2 controls with you: the score per category shows the gaps, and the activities get priorities and deadlines.
-
3
Security measure implementation
We guide you through the activities and prepare the documents management approves; the evidence is attached to the answers and the NIS 2 score records the trend.
The console in action
A tour of the console, then tasks from start to finish, on the screens you will use. Each recording is split into chapters: pick one to start from there.
NIS 2: Rules and Requirements for Businesses
The NIS 2 Directive sets a high common level of cybersecurity across the European Union. It raises the security requirements in several sectors and widens the scope to a large number of companies, including small and medium enterprises in certain sectors.
Highly critical sectors
- Public Administration
- waste water management
- banking sector
- energy
- digital infrastructure
- drinking water supply & distribution
- healthcare
- space
- financial market infrastructure
- transportation
- ICT service management


Critical sectors
- waste management
- medical device manufacturing
- food sector
- digital services
- postal and courier services
- scientific research
Key Figures on NIS 2
80+
types of entities covered by the legislation
160k+
Companies within the NIS 2 scope
27
EU member states where the directive is in force
2%
penalties of up to 2% of company turnover
Depending on size and sector, entities are classed as 'essential' or 'important', with different obligations, constraints and penalties. To avoid penalties they must meet the deadlines set by D.Lgs. 138/2024, which from 2026 brings the notification duty and the baseline security measures into force.
Article 24(2) of D.Lgs. 138/2024 sets out the security areas where the defence measures required for conformity must be put in place.

Incident handling

Business Continuity and Disaster Recovery
Specialized NIS 2 services
Dedicated solutions for the most critical aspects of NIS 2 compliance.
Incident notification
A guided flow to prepare the reports on significant incidents within the NIS 2 deadlines: early warning, incident notification and final report.
Learn moreDocumentation audit
A review of the documentation NIS 2 requires, with the findings and a plan to close the gaps.
Learn moreDelivered through Cyber Console
The whole NIS 2 compliance path (controls, actions, documentation and incident notification) is managed on Cyber Console, the platform we deliver our services from.
Explore the platform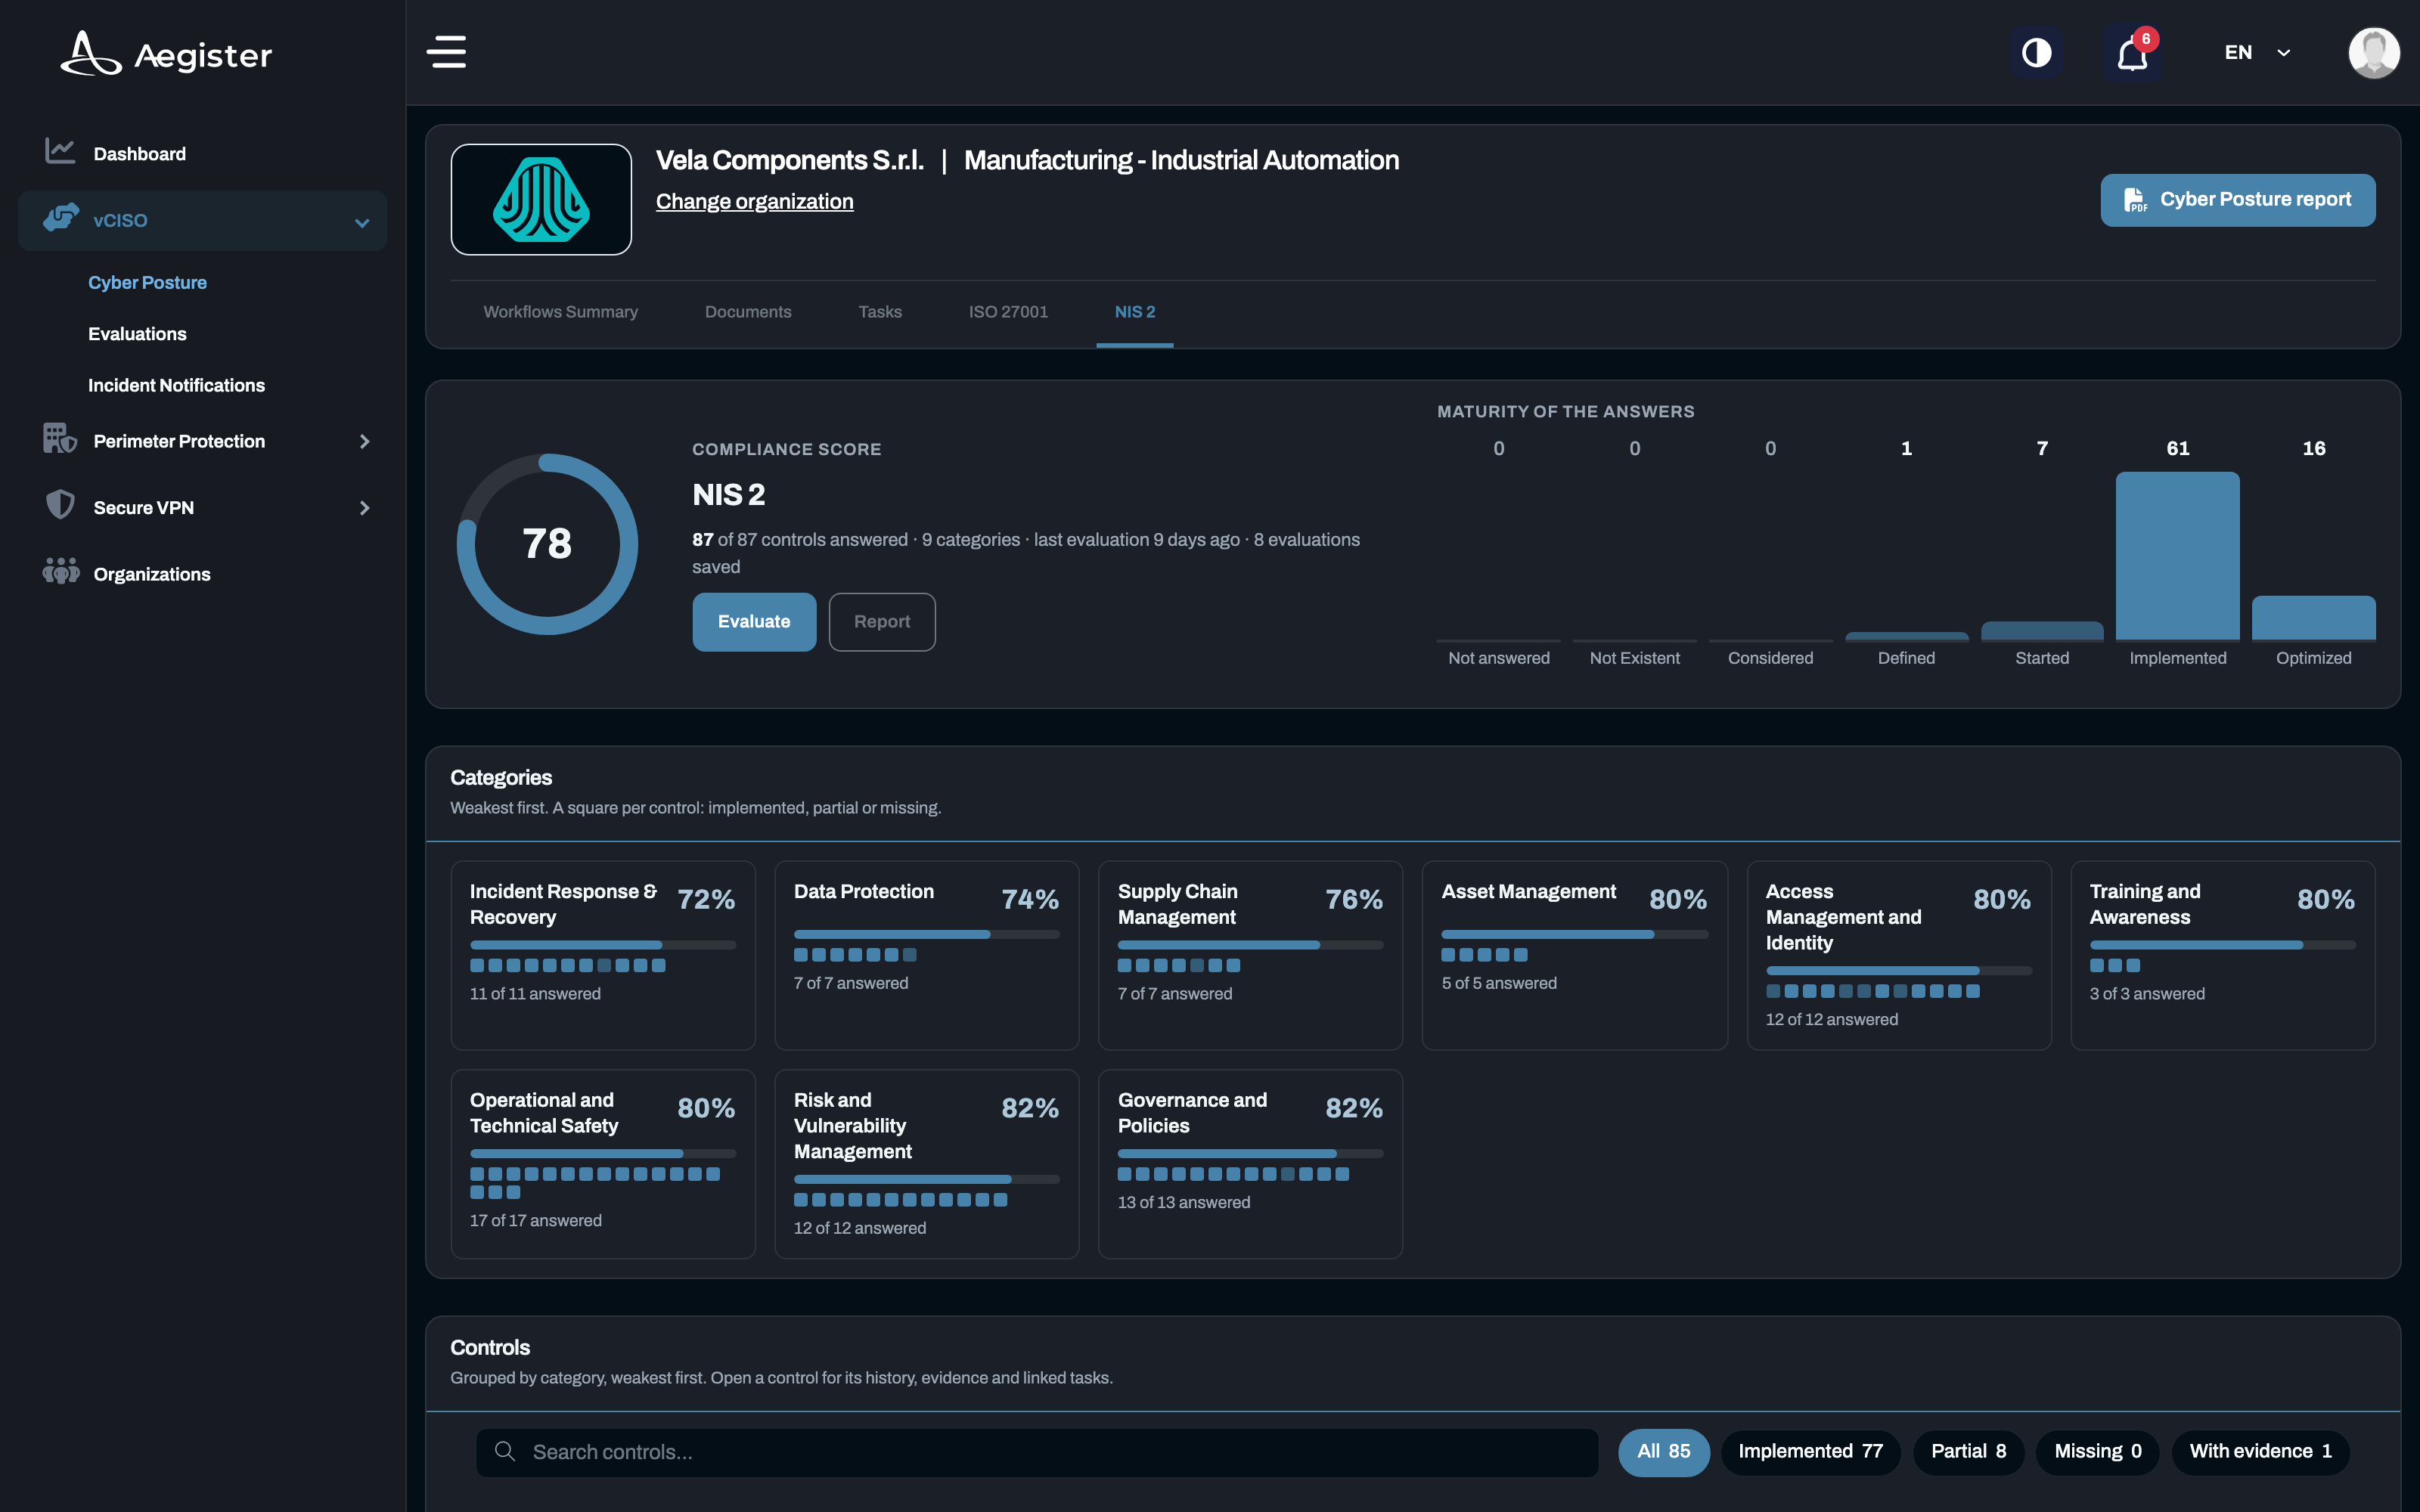
Is your company in scope of NIS 2?
Two choices, sector and size, for an indicative outcome with the article of Legislative Decree 138/2024 that sets it.
Indicative outcome
NIS 2 frequently asked questions
The NIS 2 Directive (Network and Information Security 2) is the EU regulation that establishes cybersecurity requirements for organizations operating in essential and important sectors. It replaces NIS1, expanding the scope of obligated entities and strengthening governance, risk management and incident notification obligations.
NIS 2 applies to essential and important entities across 18 sectors, including energy, transport, healthcare, digital infrastructure, public administration, space and ICT supply chain. In Italy, ACN manages the register of obligated entities and compliance deadlines.
Italian organizations were required to register with ACN by 28 February 2026. The deadline for baseline measures compliance is October 2026.
Mandatory documents include: cybersecurity policies, security organization, risk assessment, risk treatment plan, incident management plan, business continuity plan, disaster recovery plan and supplier register. The cybersecurity policy and the risk management framework must be approved by the management body.
The cost varies based on organization size and current maturity level. Aegister offers a Virtual CISO service and documentation audit that help identify gaps and build an efficient compliance plan, reducing costs compared to an unstructured approach.
NIS 2 Insights
Guides, analysis and updates on the NIS 2 Directive and compliance obligations.
 Made with AI
13 Oct 2026
NIS 2 amendments: what the Commission proposes
There is no NIS 3. On 20 January 2026 the Commission proposed targeted amendments to NIS 2 (COM(2026) 13): a small mid-cap category that would make many Annex I companies important rather than essential, scope changes, harmonised ransomware data, cyber posture certification and an ENISA role in cross-border supervision. With the Digital Omnibus single entry point, where the procedure stands as of 8 October 2026 and what still applies in Italy.
 Made with AI
10 Oct 2026
ACN supervision under NIS 2: inspections, orders and fines
For entities placed on the NIS list in April 2025, ACN gives October 2026 as the deadline for the baseline measures. How ACN supervises after that: monitoring and self-assessments, ex ante inspections for essential entities and ex post for important ones, orders and formal notices, fines up to 2% of turnover. With the deadlines for each cohort, late registrations included, and a checklist for the evidence file.
 Made with AI
09 Oct 2026
NIS 2 assessment: a self-assessment checklist for SMEs
Your company has just found out it falls under NIS 2. A self-assessment to run before an ACN review or an external audit: confirm scope, find the measures for essential or important entities, answer a checklist by function with the evidence for each question, score the gaps and decide what to fix first.