


Compliance
We guide you in keeping your company compliant with the directives in force.
Voucher MIMIT code VCCFA2600000933-D9How it works
Two paths, NIS 2 compliance and ISO 27001 certification: the Virtual CISO guides you step by step and all the work stays in Cyber Console.
Regulatory compliance
We support you at every stage of the compliance journey, with a dedicated platform and consulting.
NIS 2
Incident notification · Documentation audit
NIS 2 Directive compliance, with incident notification and the documentation audit handled in Cyber Console.
Learn moreISO 27001
Certification · Gap analysis · Cyber Console
ISO 27001 implementation and certification with Cyber Console for controls and documentation management.
Learn moreOur compliance services
From the NIS 2 Directive to ISO/IEC 27001 certification: analysis, documentation, incident notification and governance over time.
Incident notification
A guided flow to prepare the reports on significant incidents within the NIS 2 deadlines: early warning, incident notification and final report.
Learn moreDocumentation audit
A review of the documentation NIS 2 requires, with the findings and a plan to close the gaps.
Learn moreVirtual CISO
An external CISO who leads your company's governance, risk and compliance work, without the cost of an in-house hire.
Learn moreKey Regulations and Compliance Frameworks
The NIS 2 Directive and the ISO/IEC 27001 standard set the framework for business continuity, data protection and cyber risk management: the first is a legal obligation, the second a voluntary, certifiable standard.
Compliance
Compliance in information security means adopting the regulations, standards and guidelines set by public bodies and industry organisations to protect a company's information and digital infrastructure. Staying compliant avoids penalties and interruptions to the business.

NIS 2 Directive conformity
The NIS 2 Directive sets a high common level of cybersecurity across the European Union. Italy transposed it with D.Lgs. 138/2024, under Article 41(1) of Directive (EU) 2022/2555.
Learn more
NIS 2 in numbers
18
sectors covered by the directive
10
areas of security measures to adopt
27
EU member states where the directive is in force
2%
penalties of up to 2% of company turnover
ISO/IEC 27001 certification
ISO/IEC 27001 is the international standard for information security management. Certification shows, through an accredited body's audit, that the organisation manages the risks to its data and systems under a recognised model.
Learn more
Don't know where to start?
Our Cyber Check-up analyzes your security posture and recommends the most suitable solutions.
Start the Cyber Check-upDelivered through Cyber Console
Controls, remediation and documentation for NIS 2 and ISO 27001 stay on Cyber Console, together with the incident notification workflow.
Explore the platform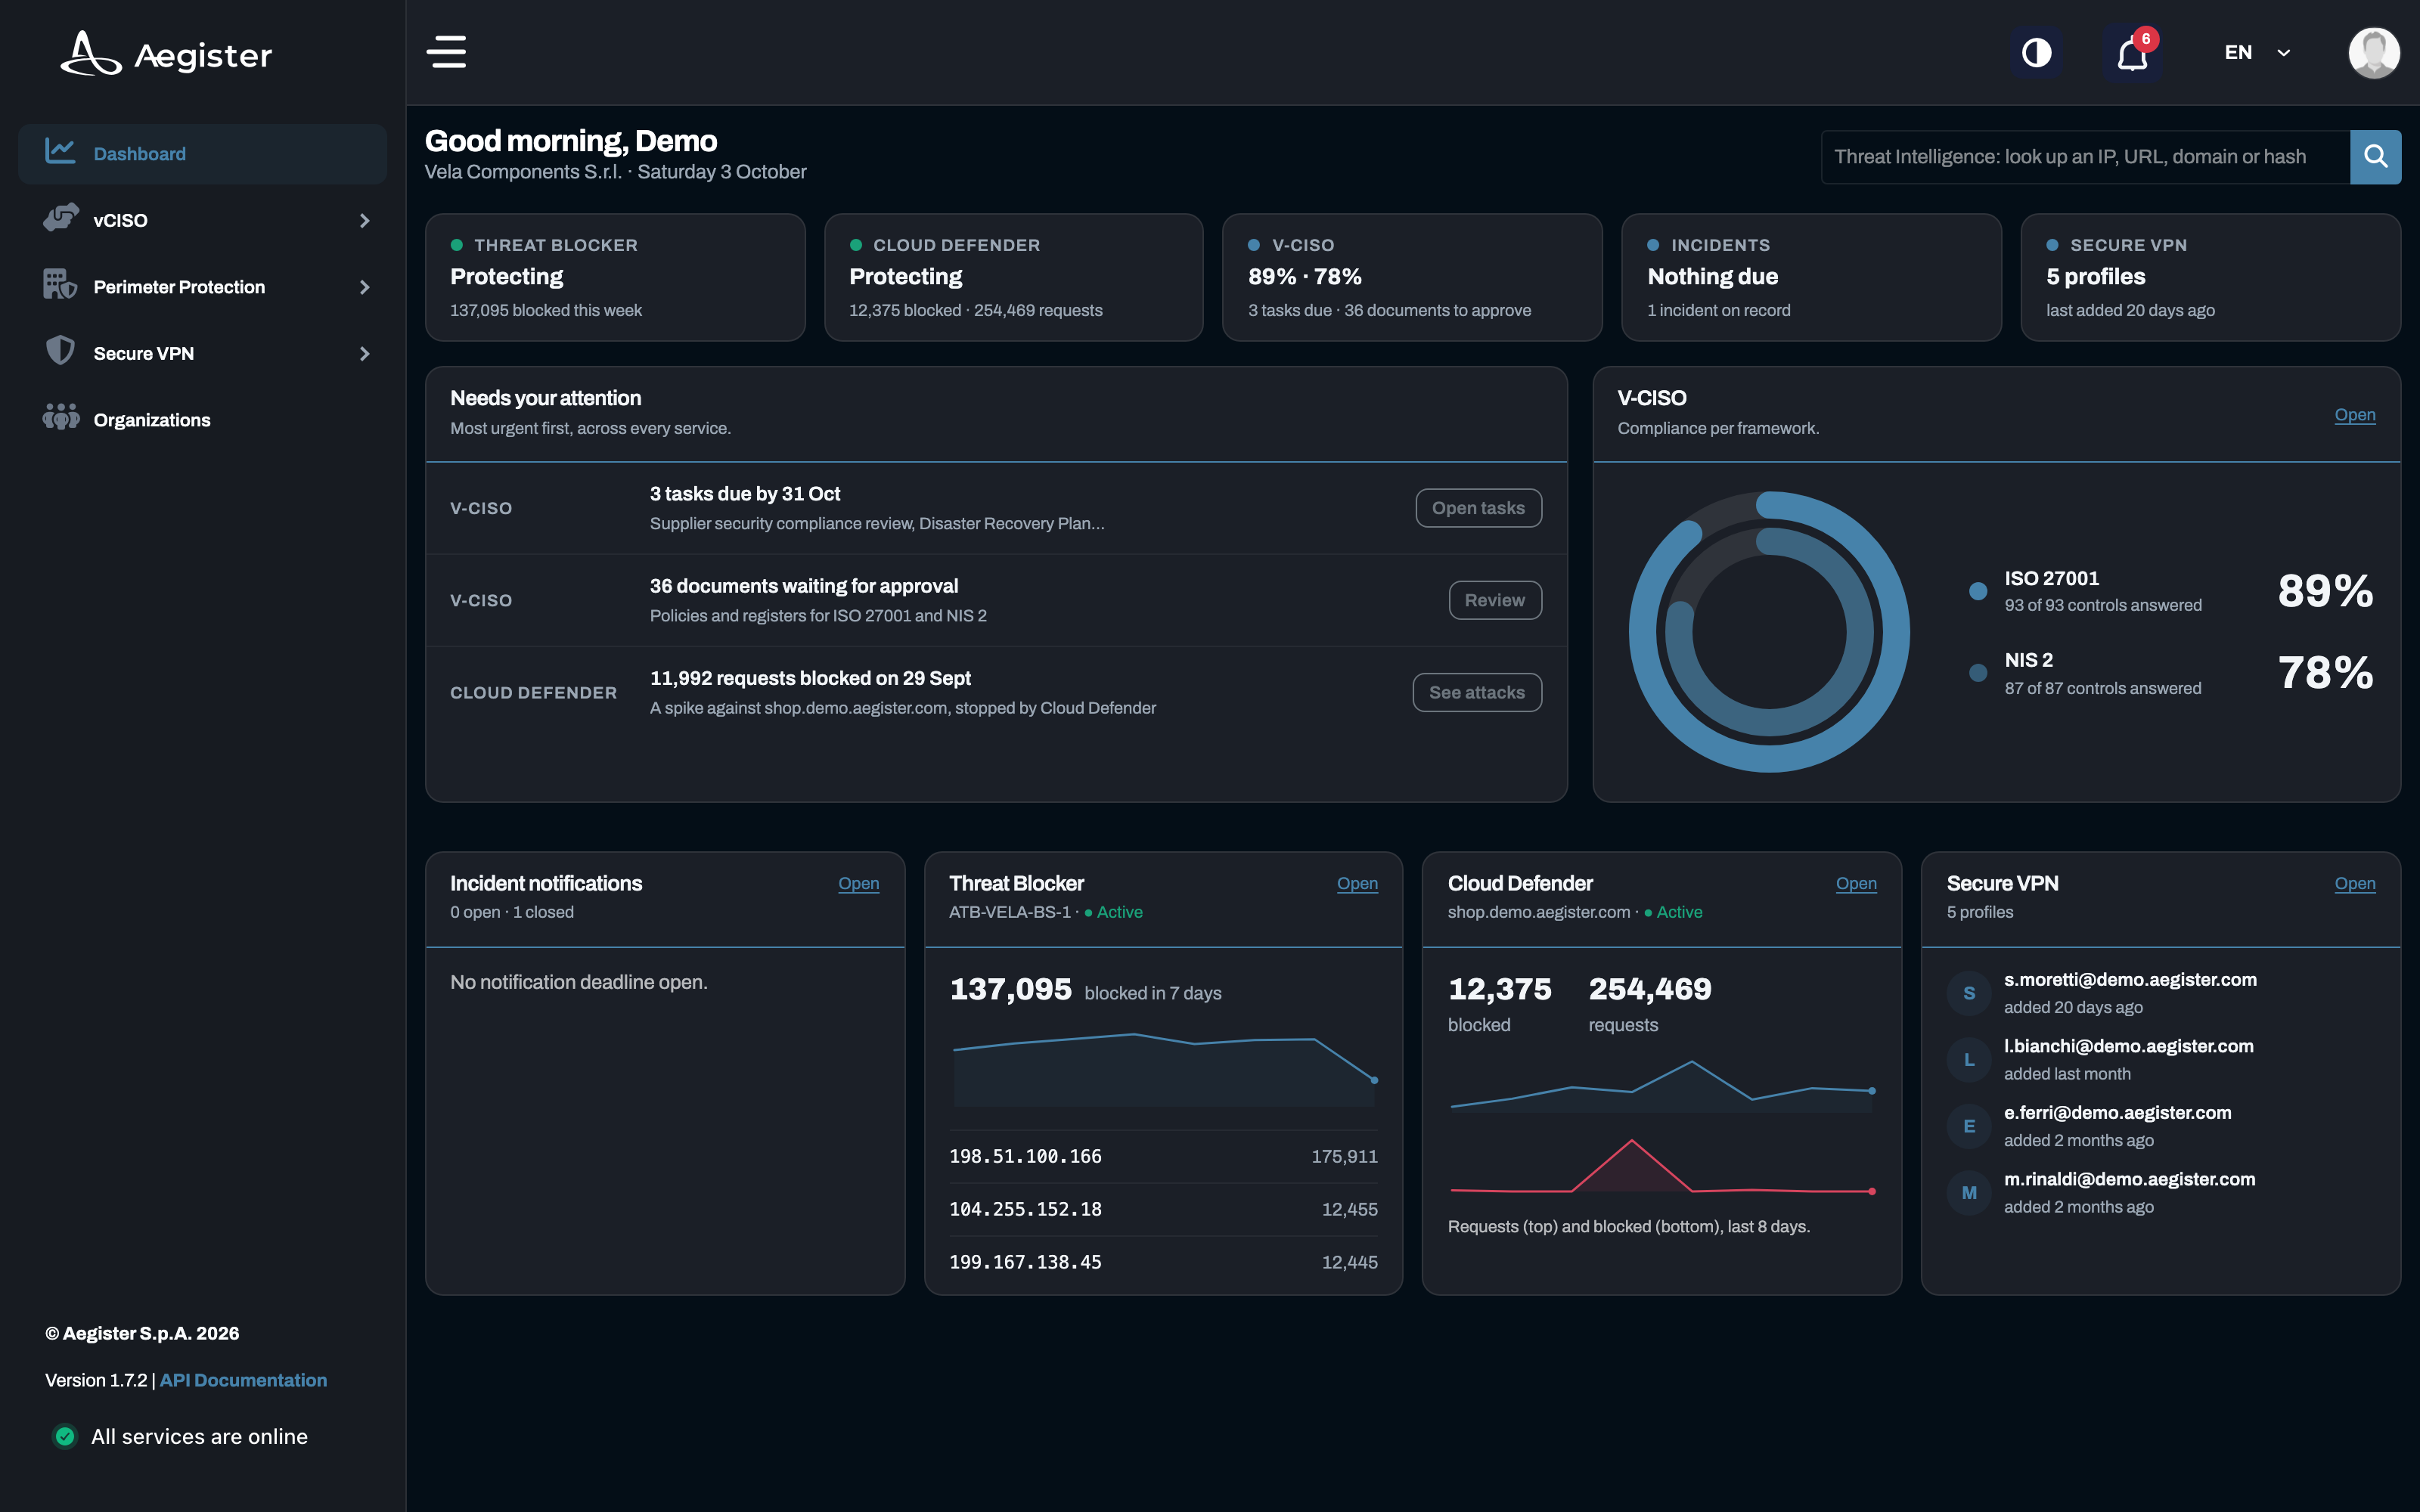
Compliance FAQ
We support companies in complying with the NIS 2 Directive (requirements analysis, security measures, incident notification and documentation audit) and on the path to ISO/IEC 27001 certification. A Virtual CISO can look after governance and compliance over time. Controls, remediation and documentation stay on Cyber Console.
NIS 2 is a legal obligation for the entities within its scope, with measures and deadlines set by ACN. ISO/IEC 27001 is a voluntary standard, certified by an accredited body. An ISO 27001 management system covers most of the NIS 2 baseline measures and produces their evidence, but it does not replace legal duties such as registration and incident notification.
Legislative Decree 138/2024 requires an early warning to CSIRT Italia within 24 hours of becoming aware of a significant incident, a notification within 72 hours and a final report within one month of the notification. Our incident notification service guides the preparation of these communications.
With the Cyber Check-up, a self-assessment that returns the company's cyber profile and its priorities. From there you decide whether to start with NIS 2 remediation, an audit of the existing documentation or the ISO 27001 path.
Compliance insights
Guides, analysis and updates on regulatory compliance and cybersecurity.
 Made with AI
13 Oct 2026
NIS 2 amendments: what the Commission proposes
There is no NIS 3. On 20 January 2026 the Commission proposed targeted amendments to NIS 2 (COM(2026) 13): a small mid-cap category that would make many Annex I companies important rather than essential, scope changes, harmonised ransomware data, cyber posture certification and an ENISA role in cross-border supervision. With the Digital Omnibus single entry point, where the procedure stands as of 8 October 2026 and what still applies in Italy.
 Made with AI
10 Oct 2026
ACN supervision under NIS 2: inspections, orders and fines
For entities placed on the NIS list in April 2025, ACN gives October 2026 as the deadline for the baseline measures. How ACN supervises after that: monitoring and self-assessments, ex ante inspections for essential entities and ex post for important ones, orders and formal notices, fines up to 2% of turnover. With the deadlines for each cohort, late registrations included, and a checklist for the evidence file.
 Made with AI
09 Oct 2026
NIS 2 assessment: a self-assessment checklist for SMEs
Your company has just found out it falls under NIS 2. A self-assessment to run before an ACN review or an external audit: confirm scope, find the measures for essential or important entities, answer a checklist by function with the evidence for each question, score the gaps and decide what to fix first.