


Cloud Defender
Protection for web applications and APIs with our cloud Web Application Firewall.
Voucher MIMIT code VCCFA2600000933-C3How it works
Activation takes minutes and does not touch your application code. In the first weeks we tune the rules against your real traffic.
-
1
Edge
Your site's DNS points to secure.aegister.com: requests reach our edge first, which handles the TLS certificates and DDoS protection.
-
2
Direct-access lock
Your server accepts only traffic that comes through Cloud Defender: anyone trying to reach it directly, for example by scanning its IP address, is blocked.
-
3
WAF rules
The rules for SQL injection and cross-site scripting are tuned to your traffic in the first weeks, so that legitimate users are not blocked.
-
4
Threat intelligence
Requests from IP addresses flagged by our threat intelligence are blocked before they reach your server. The list updates automatically.
Threats stopped, on the map
In Cyber Console the Cloud Defender map shows where the malicious requests blocked before reaching your site come from.
The console in action
A recording of the console, in chapters: pick one to start from that point.
Complete protection for your applications
Cloud Defender is a Web Application Firewall (WAF) that protects your websites and APIs from SQL injection, cross-site scripting (XSS), malicious bots and DDoS attacks.
The rules are customisable and updated by our threat intelligence: HTTP and HTTPS traffic is analysed in real time and requests that match a rule are blocked.
A WAF with our threat intelligence
Every request is checked in real time against our lists of indicators of compromise and IP reputation.
SQL Injection
Automatic blocking of SQL injection and database manipulation attempts.
XSS
Protection from Cross-Site Scripting and malicious code injection.
DDoS
DDoS attack mitigation with rate limiting and traffic analysis.
Bot Protection
Detection and blocking of malicious bots, scrapers and harmful crawlers.
Integrated threat intelligence
Cloud Defender draws on our threat intelligence network: IP reputation and threat feeds updated in real time.
Your applications behind a managed WAF
Delivered through Cyber Console
Cloud Defender is part of the perimeter protection delivered through Cyber Console: blocked threats and protection status are in the platform, alongside controls, activities and audit-ready documentation.
Explore the platform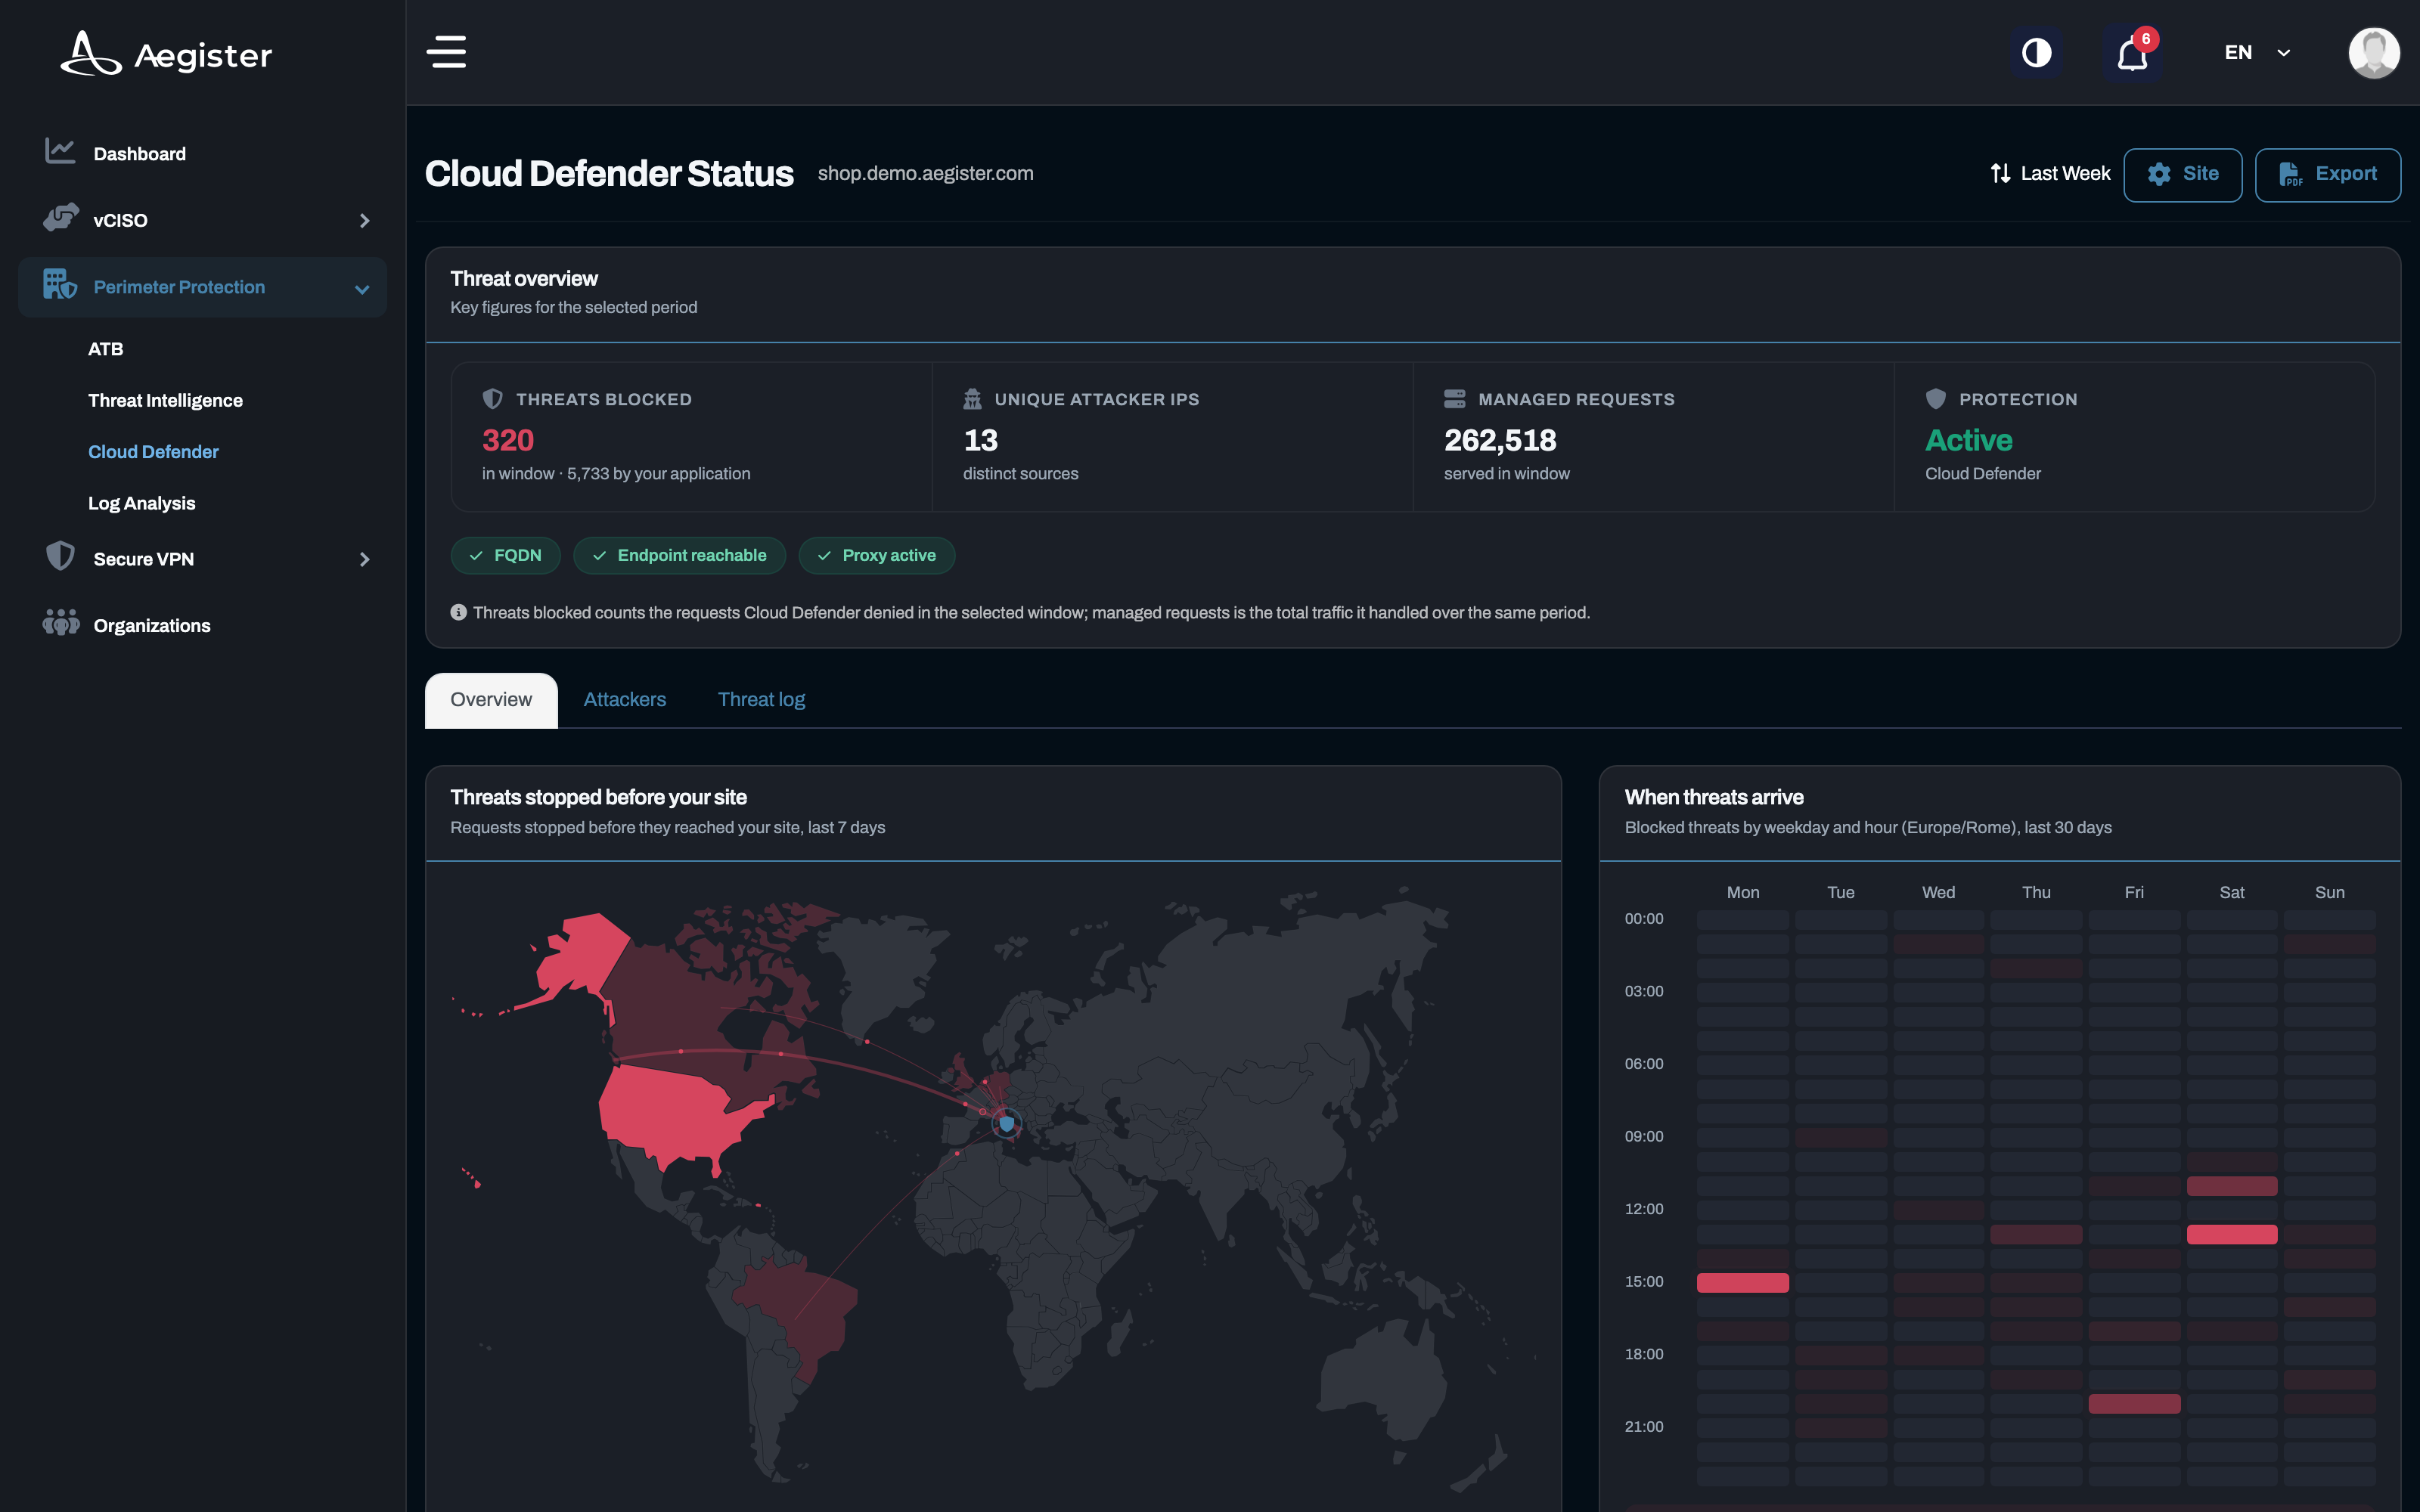
Cloud security insights
Guides and insights on cloud security, WAF and web application protection.
 Made with AI
16 Oct 2026
Cloud and cybersecurity voucher: how to check the approved supplier
The cloud and cybersecurity voucher funds only purchases from approved suppliers. Who can be one, how the list is consulted, what codes and types tell you, resellers, integrators and linked suppliers, and the questions to ask a supplier before signing the application.
Made with AI
14 Oct 2026
Cloud and cybersecurity voucher: eligible costs, case by case
What the cloud and cybersecurity voucher can buy, case by case: servers, ERP and CRM, SaaS, e-learning, artificial intelligence, professional services, VPNs, third-party products and MSP licences, with the official MIMIT FAQ answer and the condition attached to it.
 Made with AI
08 Oct 2026
Catastrophe insurance and the cloud and cybersecurity voucher: the self-declaration to attach
For the Cloud & Cybersecurity Voucher, the business declares in its application that it complies with the catastrophe insurance obligation and attaches a self-declaration (DSAN). This guide explains the requirement, the three boxes of the DSAN, the deadlines by business size, leased or rented assets and the check at disbursement stage.