


Threat Blocker
The power of threat intelligence, all in one device.
Voucher MIMIT code VCCFA2600000933-A1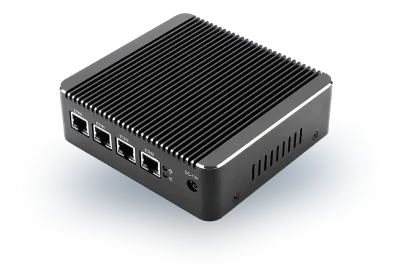
How it works
Threat Blocker receives the list of malicious IP addresses from our threat intelligence and blocks connections to and from them. It installs in two ways.
Next to your firewall: the device connects to one of its ports, gives it the up-to-date list of malicious IPs and collects its logs. Your firewall applies the block.
In place of the firewall: the device sits on the line between the internet and your network and blocks connections to and from malicious IPs itself.
Threats stopped, on the map
In Cyber Console the Threat Blocker map shows where blocked attacks come from and where stopped outbound attempts were heading.
The console in action
A tour of the console, then tasks from start to finish, on the screens you will use. Each recording is split into chapters: pick one to start from there.
Threat intelligence in action with Threat Blocker
Threat Blocker (ATB) is an appliance that protects the network perimeter with threat intelligence and IP reputation algorithms. It receives threat data from the alliance and blocks traffic to and from flagged addresses in real time, inbound and outbound. It sits alongside the systems already in your infrastructure, such as firewalls, SIEM, SOAR and WAF (Web Application Firewall), and its work is followed from Cyber Console.
Aegister S.p.A. holds the exclusive licence for Italy to OneFirewall's Cyber Threat Intelligence (CTI), which collects malicious IP addresses from World Crime Feeds (WCF), more than 130 sources. Threat Blocker blocks connections to and from those addresses, with a list updated at least once an hour.
Threat intelligence sources
The intelligence is fed by the World Crime Feeds (WCF) network, which collects data from over 130 global sources and pools the reports shared by the Alliance. It is an API-accessible database that aggregates data and indicators of compromise (IoC) in IPv4, domain and URL formats.
Threat Blocker blocks flagged IP addresses before they reach your network. Domains, URLs and files can be checked from Cyber Console and through our APIs.

Indicators of compromise
Blocked by Threat Blocker
IPv4
Malicious IP detection
From Cyber Console and APIs
Files
Hash Verification
From Cyber Console and APIs
URL
URL monitoring
From Cyber Console and APIs
Domains
Domains analysis
Why Choose It
Advanced Automation Capabilities
Connections to and from flagged IP addresses are blocked in real time, inbound and outbound, with no manual work.
Next to your firewall or in its place
In parallel mode it works next to the firewall you already run; in series mode it takes its place. Either way it works alongside your SIEM, SOAR and WAF.
Cut Down on Cybersecurity Tools and External Services
Blocking threats before they enter the company perimeter cuts the number of tools you have to run. ATB uses the threat intelligence of OneFirewall, which shares threat reports and IP reputation in real time.
Threat intelligence insights
Guides and analysis on threat intelligence and protection against cyber threats.
 Made with AI
22 May 2025
Cyber Threats in Italy - ACN Operational Summary, April 2025
The ACN's April 2025 Operational Summary highlights a rise in ransomware and DDoS attacks in Italy, with key sectors like telecoms and public administration under threat.
 Made with AI
28 Apr 2025
Understanding Threat Intelligence: What Every Business Should Know
Explore the fundamentals of threat intelligence and its importance in proactive cybersecurity strategies.
Made with AI
12 Apr 2025
Cyber Threats 2025: The Most Common Attacks and How to Defend Against Them
An in-depth look at the most common cyber threats in 2025 from ransomware to supply chain attacks and how organizations can defend themselves using standards like the NIST CSF and ACN strategy.