Many companies approach cybersecurity as a list of tools to buy, procedures to follow, and checkboxes to tick. But without strategic direction, the risk remains the same: doing a lot but not enough.
The truth is, cybersecurity requires vision, expertise, and continuous updates. However, not all companies can afford an internal Chief Information Security Officer (CISO) whether due to budget constraints or the difficulty of finding truly qualified professionals.
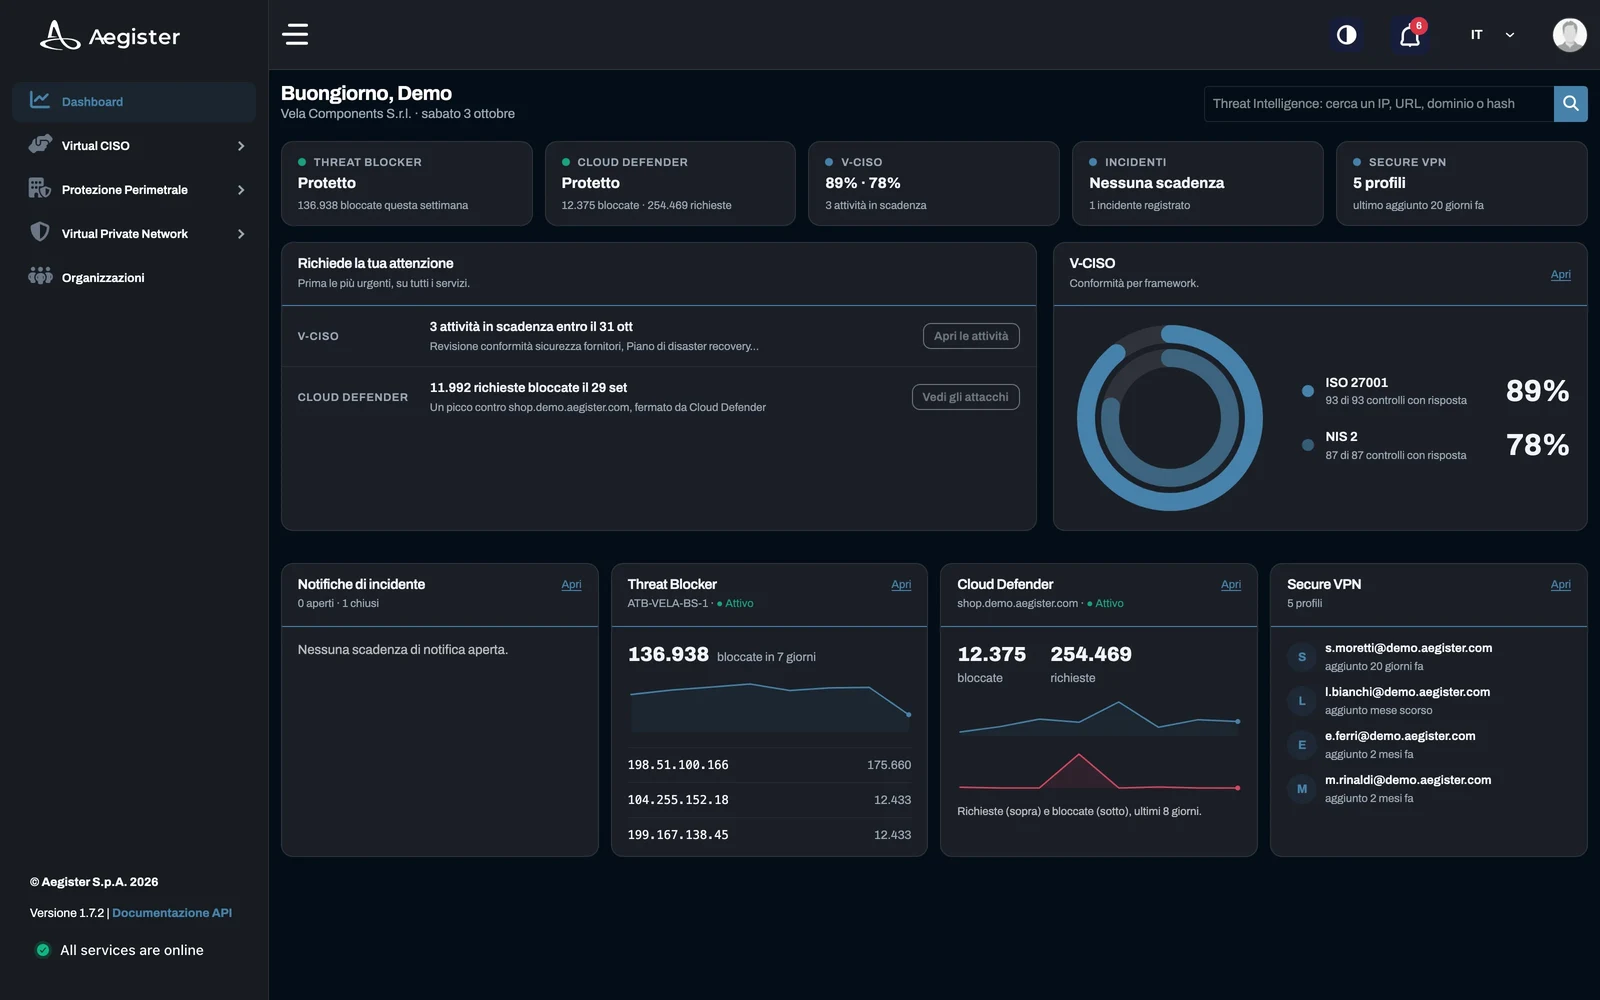
This is where Aegister's Virtual CISO comes in a cyber-human solution that works alongside your internal team, offering the same strategic guidance as a full-time CISO but in a flexible, scalable, and cost-effective model.
While threats evolve, companies that rely on Aegister's vCISO stay ahead with actionable intelligence, ready-to-execute plans, and expert guidance always on hand. Our NIS2 compliance guide helps organizations navigate the requirements effectively.
Discover how Aegister's vCISO can provide the leadership your cybersecurity program needs without compromise.