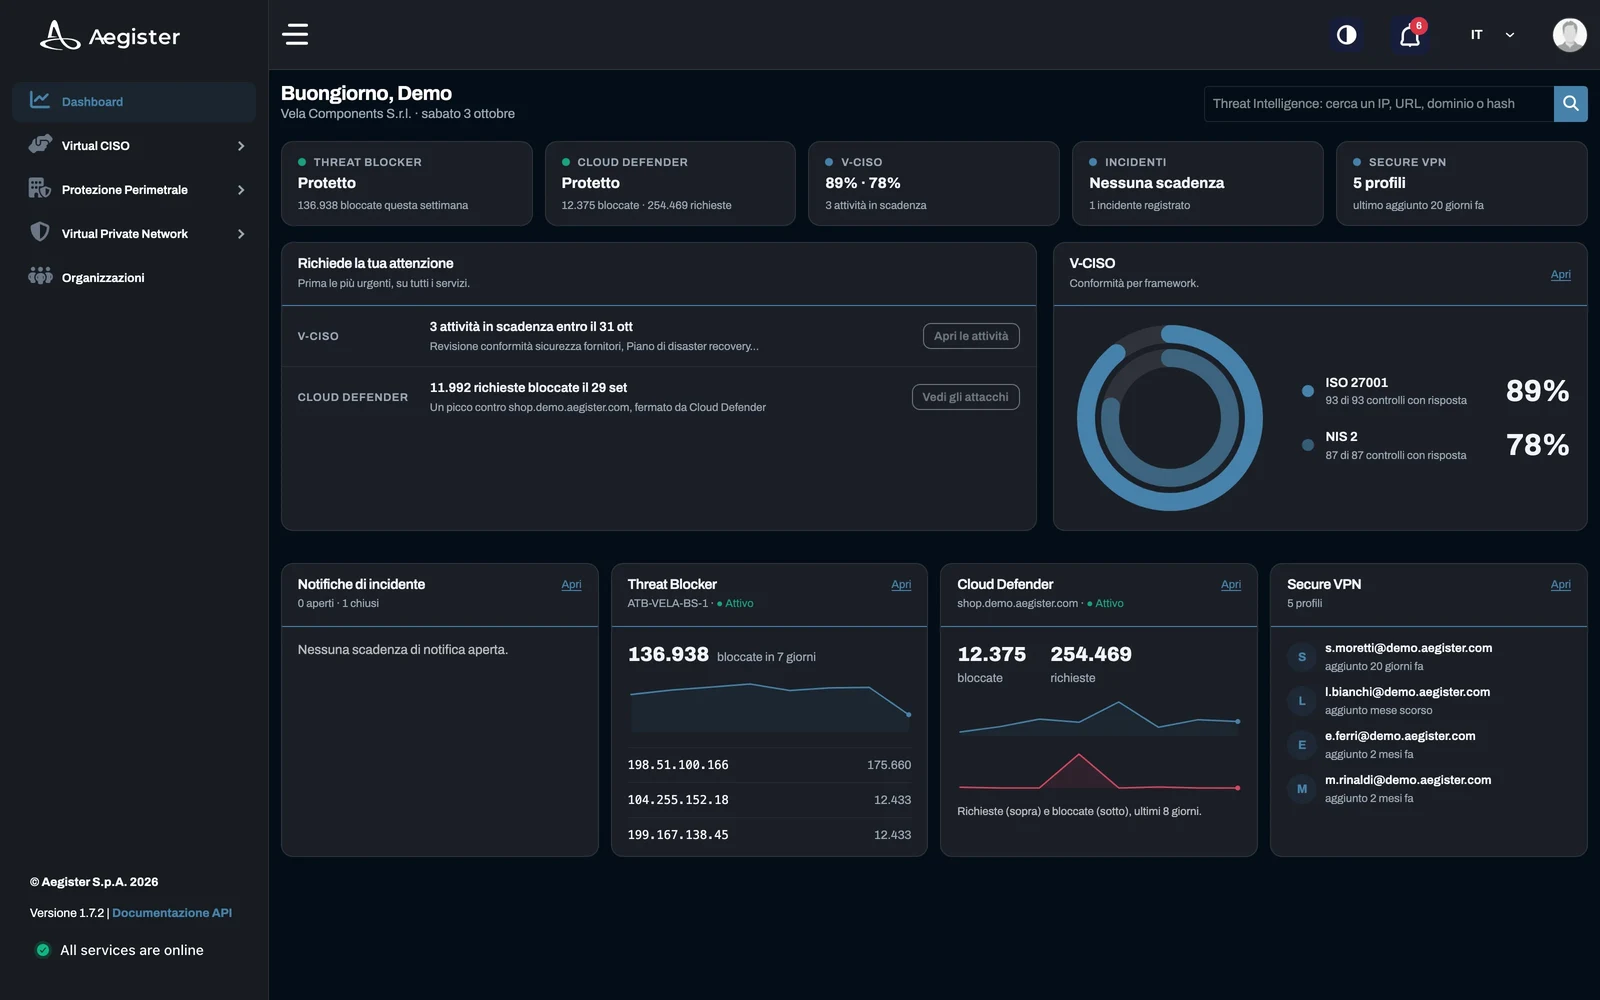
The NIS 2 Directive represents a significant step forward in the European Union's efforts to enhance cybersecurity across member states. By setting stricter requirements for compliance, the directive aims to create a unified approach to managing cyber risks and protecting critical infrastructure. For detailed information about specific obligations and deadlines, please refer to our comprehensive article on NIS2 obligations.
What Is the NIS 2 Directive?
The NIS 2 Directive is an update to the original NIS Directive, expanding its scope and introducing more stringent obligations for businesses. It focuses on improving the resilience of networks and systems, ensuring rapid response to incidents, and fostering cooperation across sectors and countries. Learn more about implementing these requirements in our detailed guide to NIS 2 compliance.
Organizations in sectors like energy, transport, finance, and healthcare are now required to implement robust cybersecurity measures and report incidents within specified timeframes.
Key Changes in NIS 2
Compared to its predecessor, the NIS 2 Directive introduces:
- Wider applicability, covering more sectors and entities.
- Stronger reporting obligations for cybersecurity incidents.
- Increased accountability for senior management regarding compliance.
- Harsher penalties for non-compliance, including fines and legal action.
These changes reflect the EU's commitment to strengthening the overall cybersecurity posture of critical and essential services.
How to Prepare for NIS 2
To comply with the NIS 2 Directive, organizations must:
- Conduct a thorough risk assessment to identify vulnerabilities.
- Implement policies and procedures that meet the directive's requirements.
- Train employees to recognize and respond to cybersecurity threats.
- Establish clear communication channels for incident reporting and response.
Early preparation is essential to avoid the risks of non-compliance and ensure smooth operations in an increasingly regulated landscape.