In today's digital landscape, cybersecurity is not just an option but a regulatory obligation. Organizations aiming to protect their data and ensure operational continuity must navigate increasingly stringent regulations. Understanding these directives is the first step toward robust business protection.
General Data Protection Regulation (GDPR)
The GDPR focuses on safeguarding personal data of individuals within the European Union. It mandates organizations to implement appropriate technical and organizational measures to ensure data privacy and security. Non-compliance can result in substantial fines and reputational damage.
Network and Information Security Directive 2 (NIS2)
The NIS2 Directive represents a significant advancement in EU cybersecurity regulations. For detailed information about specific obligations and deadlines, please refer to our comprehensive article on NIS2 obligations. The directive requires entities to adopt risk management practices, report incidents, and ensure the security of network and information systems. Learn more about implementing these requirements in our detailed guide to NIS 2 compliance.
ISO/IEC 27001
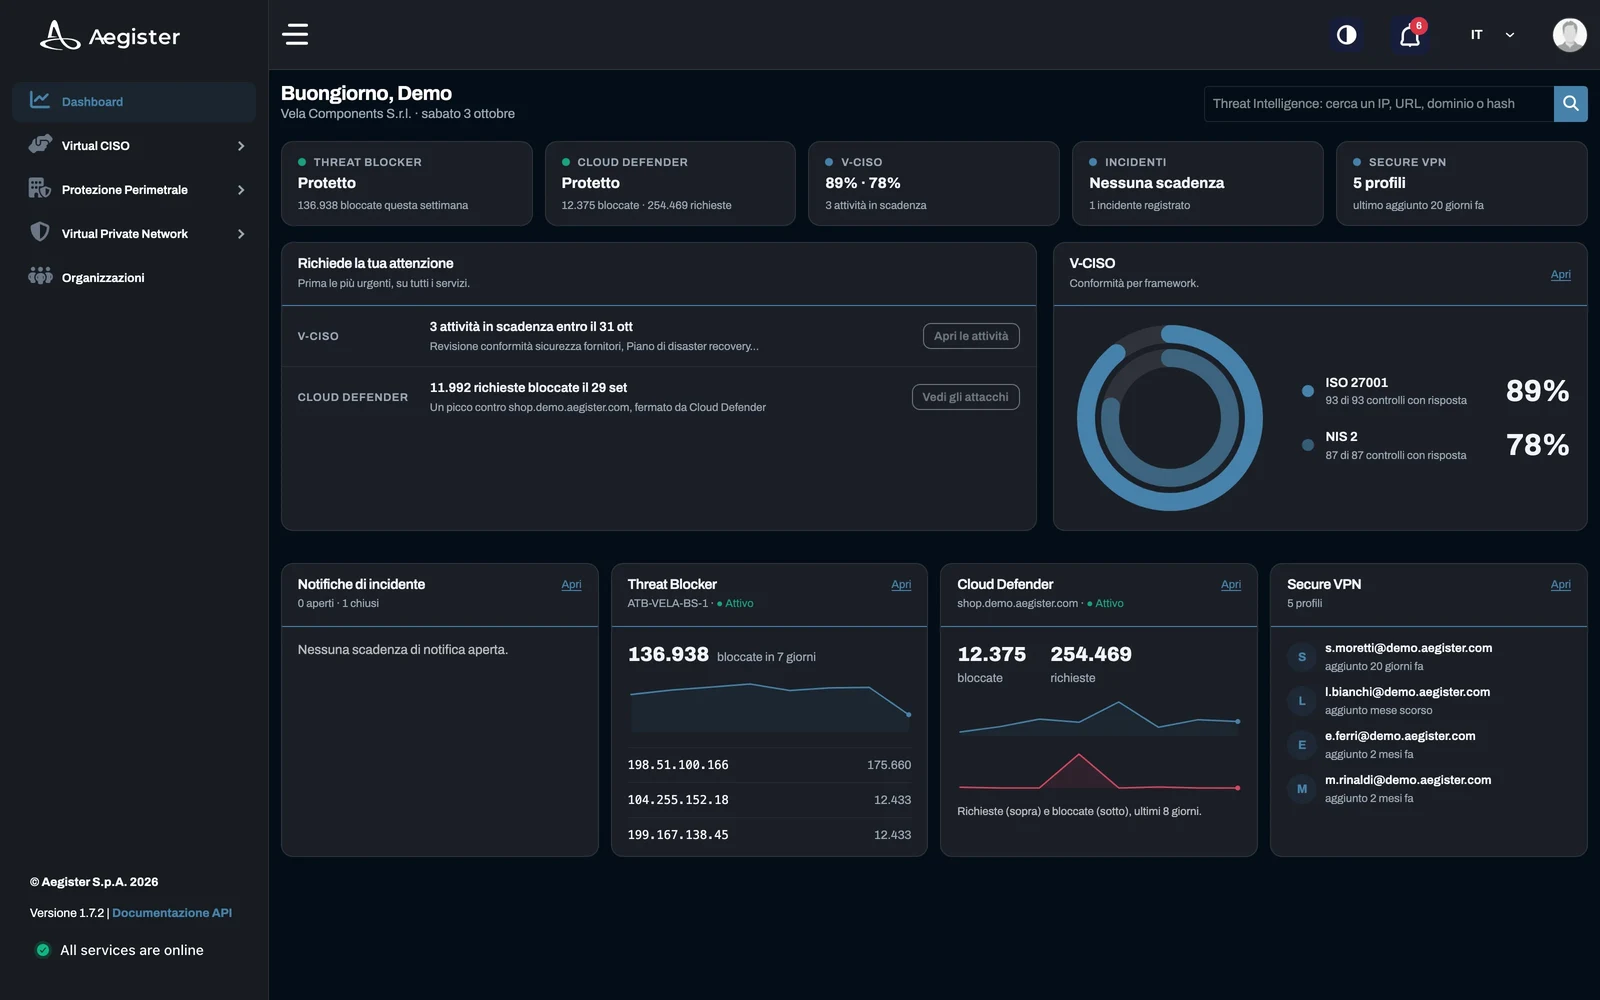
ISO/IEC 27001 is an international standard that specifies requirements for establishing, implementing, maintaining, and continually improving an information security management system (ISMS). Achieving certification demonstrates an organization's commitment to information security and can facilitate compliance with other regulations like GDPR and NIS2.
Understanding and integrating these regulations into your organization's cybersecurity strategy is vital for legal compliance and the protection of your digital assets. For organizations looking to strengthen their NIS2 compliance, the Italian Cybersecurity Agency (ACN) has defined specific baseline security measures that must be implemented. Engaging with experts and adopting recognized standards can significantly enhance your security posture. Consider exploring our Virtual CISO service for expert guidance in implementing these measures effectively.