Websites and APIs receive malicious traffic every day: requests from IP addresses known for hostile activity, attacks against the applications, DDoS attacks. Additionally, organizations must comply with increasingly stringent regulations like GDPR, NIS2, and ISO/IEC 27001.
Traffic goes through Cloud Defender first
Cloud Defender is our managed WAF: traffic to your sites and APIs goes through Cloud Defender before it reaches your server, and requests from IP addresses flagged by our threat intelligence are blocked. It is a useful building block for organizations preparing for NIS2 baseline security measures.
Aegister's Integrated Approach
In this scenario, having a partner capable of effectively managing cloud security makes a difference. Aegister doesn't just offer technological solutions; it accompanies companies with an integrated and personalized approach:
- Activation through DNS: your site's record points to secure.aegister.com, and protection is active within minutes once our side is ready.
- TLS and DDoS at the edge: handled before traffic reaches your server.
- Threat intelligence: requests from the IP addresses on our list are blocked; the list is updated every hour.
- Direct access closed: your server accepts only traffic that comes from Cloud Defender. The SQL injection and XSS rules are calibrated on your traffic before they block.
Ensuring Compliance
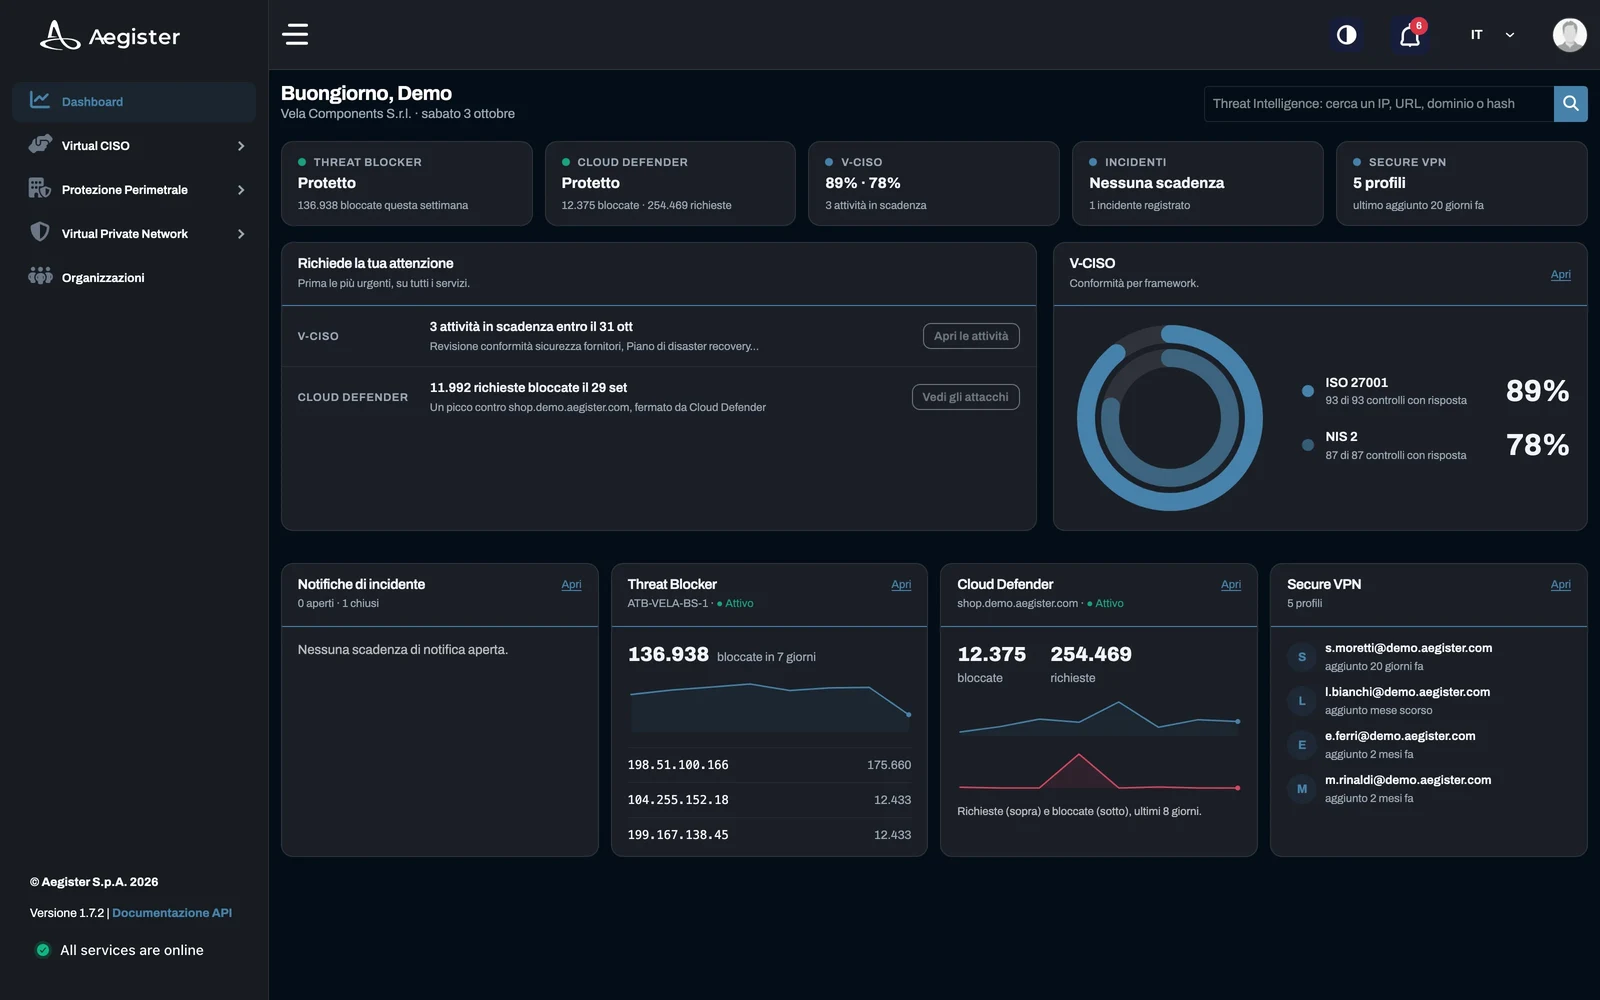
Compliance with regulations like GDPR, NIS2, and ISO/IEC 27001 is crucial. Aegister's solutions are designed to help organizations meet these standards; the blocks and the service status are available in Cyber Console. By aligning with these frameworks, businesses can demonstrate their commitment to data protection and cybersecurity.
With Aegister, the cloud becomes a secure and strategic asset.
Learn more about Cloud Defender