


Incident notification
How to recognise a significant incident and prepare the early warning, the notification and the final report within the NIS 2 deadlines.
All articles
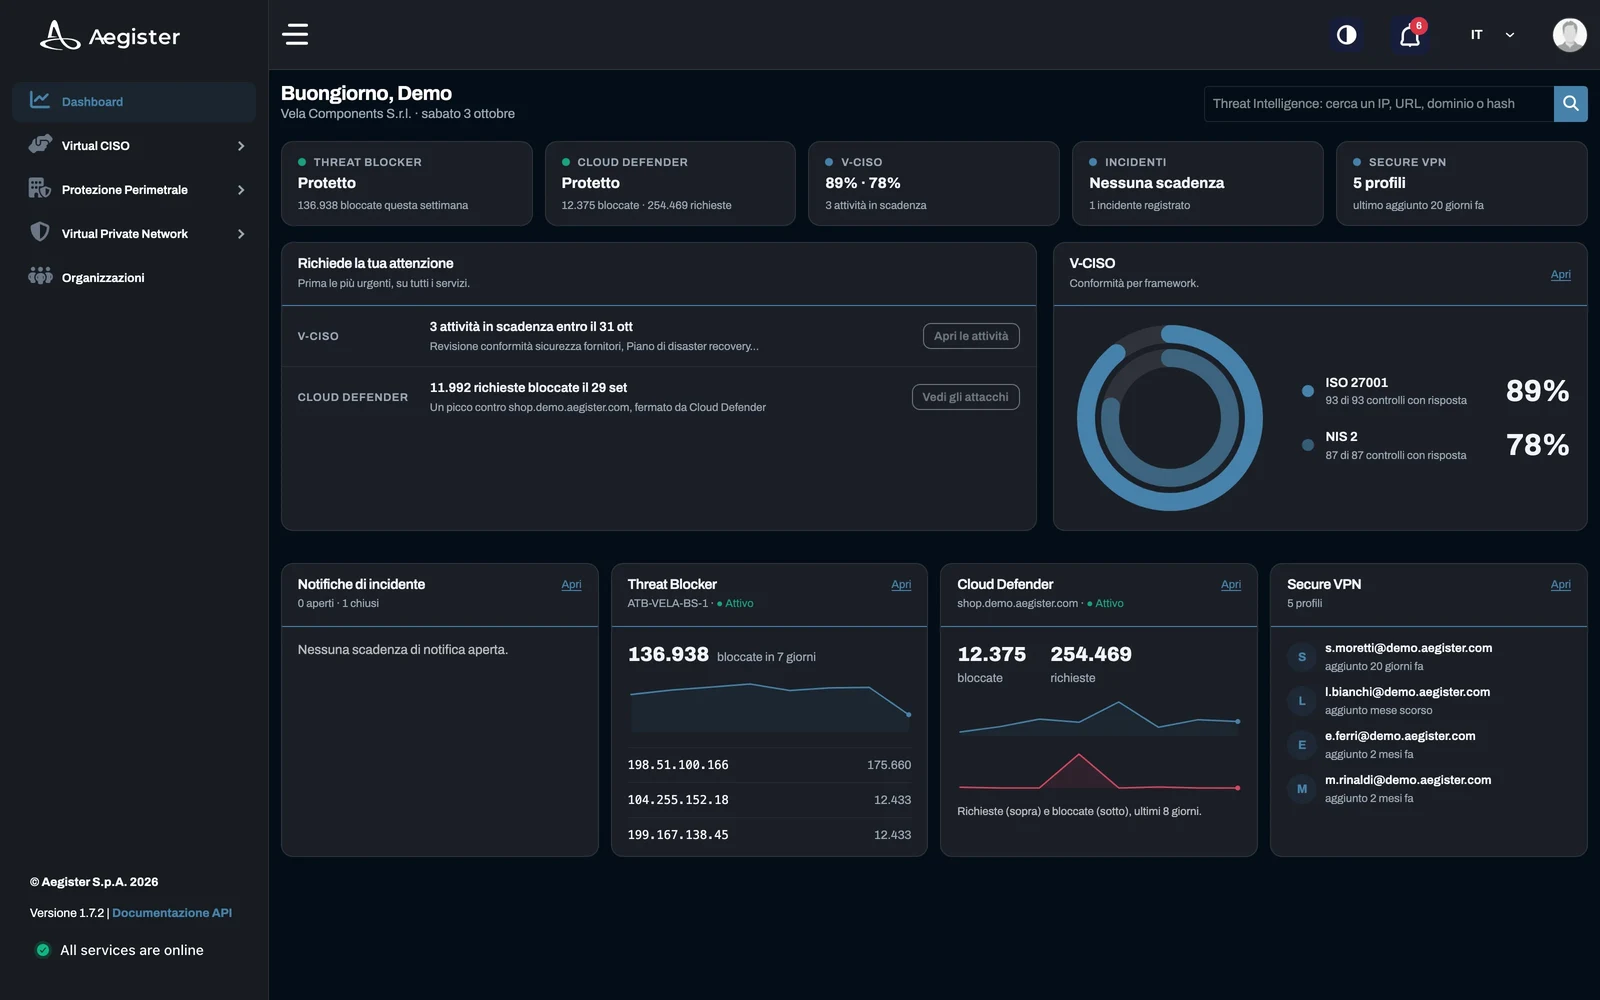
Cyber Console 2.0: redesigned from top to bottom
Cyber Console reaches version 2.0: an interface redesigned from top to bottom, one search for the whole console, video guides to using the console an…
ECCC CYBERAI Funding 2027: Secure AI for European Cyber Operations
The CYBERAI topic funds secure, trustworthy AI for detection, threat intelligence, response and self-healing in European cyber operations. How it dif…
NIS 2 vs GDPR: Key Differences and Overlap for Italian Organizations
Comparison guide for Italian organizations: how NIS 2 and GDPR differ, where they overlap, and how to coordinate incident notification when personal …
New NIS Subjects in 2026: Incident-Notification and Baseline-Measure Deadlines
The ACN 2026 timing determination sets a distinct implementation path for entities first listed in the Italian NIS perimeter during 2026: significant…
ACN NIS 2026 Platform Rules and New Deadlines: Master Overview
ACN's April 2026 package sets new NIS deadlines for subjects listed for the first time in 2026 (incident notification from 1 January 2027, baseline m…

NIS 2 Executive Board Reporting: How to Turn Audit Outputs into Governance Decisions
Practical executive reporting model for NIS 2 audit outcomes with minimum KPI set, traffic-light escalation, and evidence-based closure visibility fo…
ACN Adopts Incident Taxonomy Under Law 90/2024: What Obligated Entities Must Do Now
ACN adopted the incident taxonomy under Law 90/2024 via the Determina of 9 February 2026. Obligated entities must now report incidents within 24 hour…
NIS 2 Incident Management Documentation Review: Method, Gaps, and Remediation Priorities
Practical review model for NIS 2 incident-management documentation covering process integrity, notification readiness, role accountability, and crisi…
NIS 2 Point of Contact and CSIRT Contact Role: Accountability and Operating Duties
NIS 2 implementation guidance distinguishes the legal Point of Contact from the operational CSIRT contact role. Practical guide to role formalization…
NIS 2 Significant Incident IS-3: Violation of Expected Service Levels
IS-3 in the ACN baseline model covers service-level violation incidents affecting entity services and activities. Practical guide to qualification, s…
NIS 2 Significant Incident IS-2: Integrity Loss Affecting Digital Data
IS-2 in the ACN baseline model covers integrity loss affecting digital data under entity ownership or control. Practical guide to qualification, evid…
NIS 2 KPIs and continuous improvement: operational metrics for resilient compliance
ACN guidance frames improvement as a continuous phase across the full incident lifecycle. This guide provides a practical KPI framework, governance r…
NIS 2 Significant Incident IS-1: Confidentiality Loss Affecting Digital Data
IS-1 in the ACN baseline model covers confidentiality loss affecting digital data under entity ownership or control. Practical guide to qualification…
Common NIS 2 compliance mistakes: practical gaps that delay baseline readiness
Most NIS 2 delays are operational: missing evidence, unclear ownership, untested notification workflows, and late governance decisions. A practical g…
NIS 2 Incident Typology Model: Condition, Compromise, and Affected Object
ACN baseline guidance classifies significant incidents through condition, compromise, and object of compromise. Practical guide to using the typology…
NIS 2 incident-notification obligations are live: operating model after the 9-month deadline
The NIS 2 9-month incident-notification deadline passed in January 2026. This guide provides the post-deadline operating model: governance confirmati…
NIS 2 incident management and CSIRT notification plan: practical guide for an approvable RS.MA-01 document
The incident management plan is mandatory under NIS 2 Appendix C (RS.MA-01). This guide covers what an approvable plan must include, a practical temp…
NIS 2 crisis management plan: practical guide for an approvable ID.IM-04 document
The crisis management plan is mandatory under NIS 2 Appendix C (ID.IM-04). This guide covers what an approvable plan must contain, a practical templa…
NIS 2 Response Controls (RS): Signaling and Investigation Operating Model
The NIS 2 Response (RS) domain requires structured incident response through signaling, investigation, and iterative decision loops. Practical guide …
NIS 2 Detection Controls (DE): Event Monitoring and Adversarial Signal Handling
The NIS 2 Detection (DE) domain requires monitoring networks, services, and endpoints to identify adverse events early. Practical guide to log readin…